awesome-soc
A curated knowledge base to build, run and mature a SOC (including CSIRT).
https://github.com/cyb3rxp/awesome-soc
Last synced: 17 days ago
JSON representation
Critical sensors for a SOC
SOC architecture of detection
- Endpoint Detection and Response
- SentinelOne - us/microsoft-365/security/defender-endpoint/microsoft-defender-endpoint?view=o365-worldwide), Harfanglab, ESET XDR, WithSecure Elements EDR, CrowdStrike Falcon EDR, Tanium, Wazuh
- Gartner reviews and ratings
- Microsoft Defender for Office365 - reference/email-gateway), Mimecast, WithSecure Elements Collaboration Protection
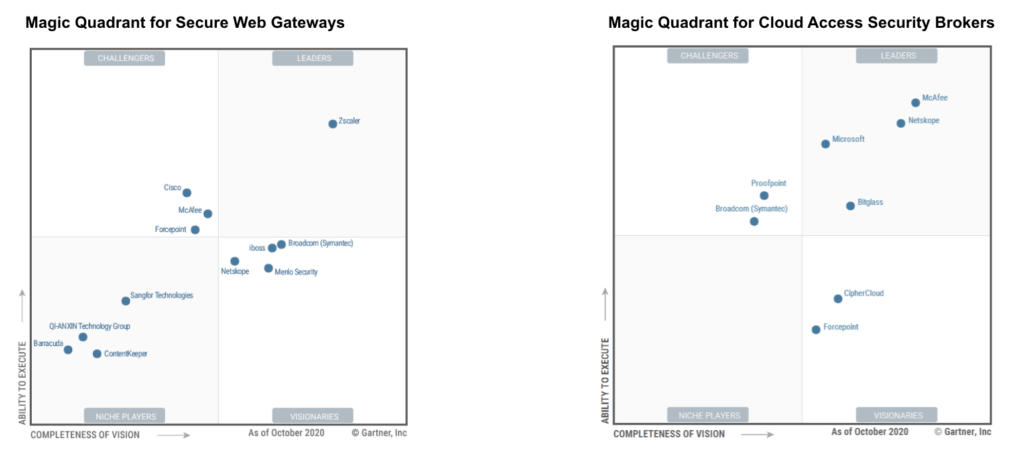
- Secure Web Gateway
- BlueCoat Edge SWG - access-service-edge-sase/index.html), Zscaler Cloud proxy, Netskope.
- Identity Threat Detection and Response
- Semperis Directory Services Protector
- Intrinsec (in French) - surface-management), Qualys EASM
- ImmuniWeb
- Cloud Access Security Broker
- Gartner magic quadrant
- Microsoft MCAS - white-papers-data-protection-challenges?_bt=534426399999&_bk=%2Bzscaler%20%2Bcasb&_bm=b&_bn=g&_bg=121807608181&utm_source=google&utm_medium=cpc&utm_campaign=google-ads-na&gclid=CjwKCAjwu5yYBhAjEiwAKXk_eKLlKaMfJ-oGYItPTHguAmCA_b9WP0zNZgLPqGKjfC19IGmQFFG_9RoCgJAQAvD_BwE), Netskope.
- AD decoy acounts - directory-a-canary-under-your-hat/)
- Gartner magic quadrant - nurture-2023_2/report-forrester-wave-endpoint-security-q4-2023?cid=emm%7Cb%7Chubspot%7Cnrt-epp-2023&utm_campaign=nurture-epp-2023&utm_medium=email&_hsmi=280555694&utm_content=280555694&utm_source=hs_automation)
- Gartner magic quadrant - engenuity.org/), and Forrester Wave
- Semperis Purple Knight
- Microsoft Defender - more-about-endpoint-protection/), BitDefender.
- Secure Email Gateway
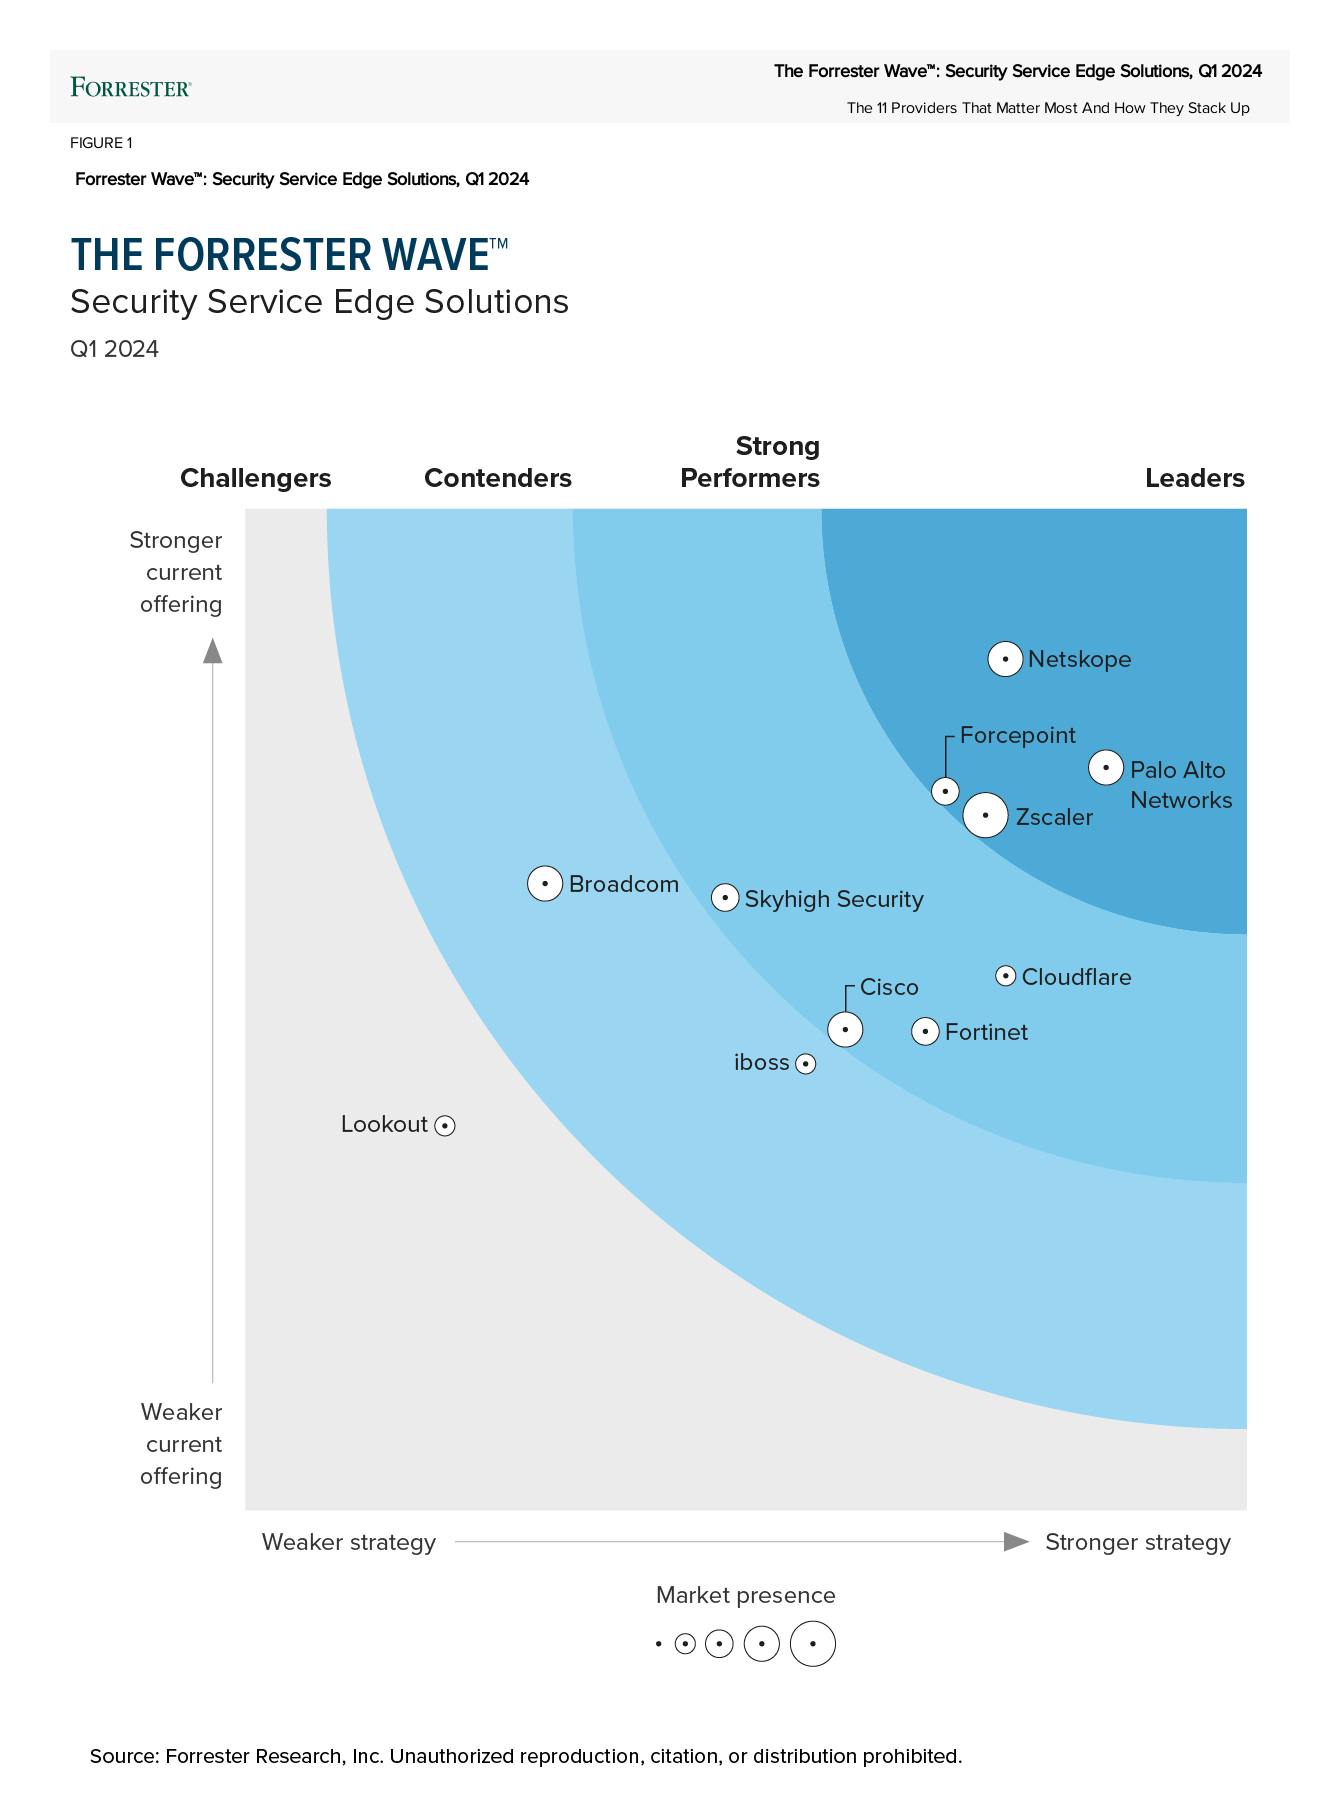
- Forrester wave for SSE
- Identity Threat Detection and Response
- Gartner magic quadrant - nurture-2023_2/report-forrester-wave-endpoint-security-q4-2023?cid=emm%7Cb%7Chubspot%7Cnrt-epp-2023&utm_campaign=nurture-epp-2023&utm_medium=email&_hsmi=280555694&utm_content=280555694&utm_source=hs_automation)
- latest Forrester Wave about MTD
- Zimperium MTD
- Gartner magic quadrant - engenuity.org/), and Forrester Wave
- Semperis Purple Knight
- Gartner magic quadrant
- Semperis Purple Knight
- Gartner magic quadrant - nurture-2023_2/report-forrester-wave-endpoint-security-q4-2023?cid=emm%7Cb%7Chubspot%7Cnrt-epp-2023&utm_campaign=nurture-epp-2023&utm_medium=email&_hsmi=280555694&utm_content=280555694&utm_source=hs_automation)
- Intrinsec - surface-management), Qualys EASM

Critical tools for a SOC/CSIRT
SOC architecture of detection
- SIEM
- SOA
- SwimLane - project.org/), PAN Cortex XSOAR
- TIP
- Gartner magic quadrant
- overview of SOAR providers
- Gartner magic quadrant - 2HXU226Z&ct=240626&st=sb)
- SOAR Data quadrant awards
- Gartner magic quadrant - 2HXU226Z&ct=240626&st=sb)
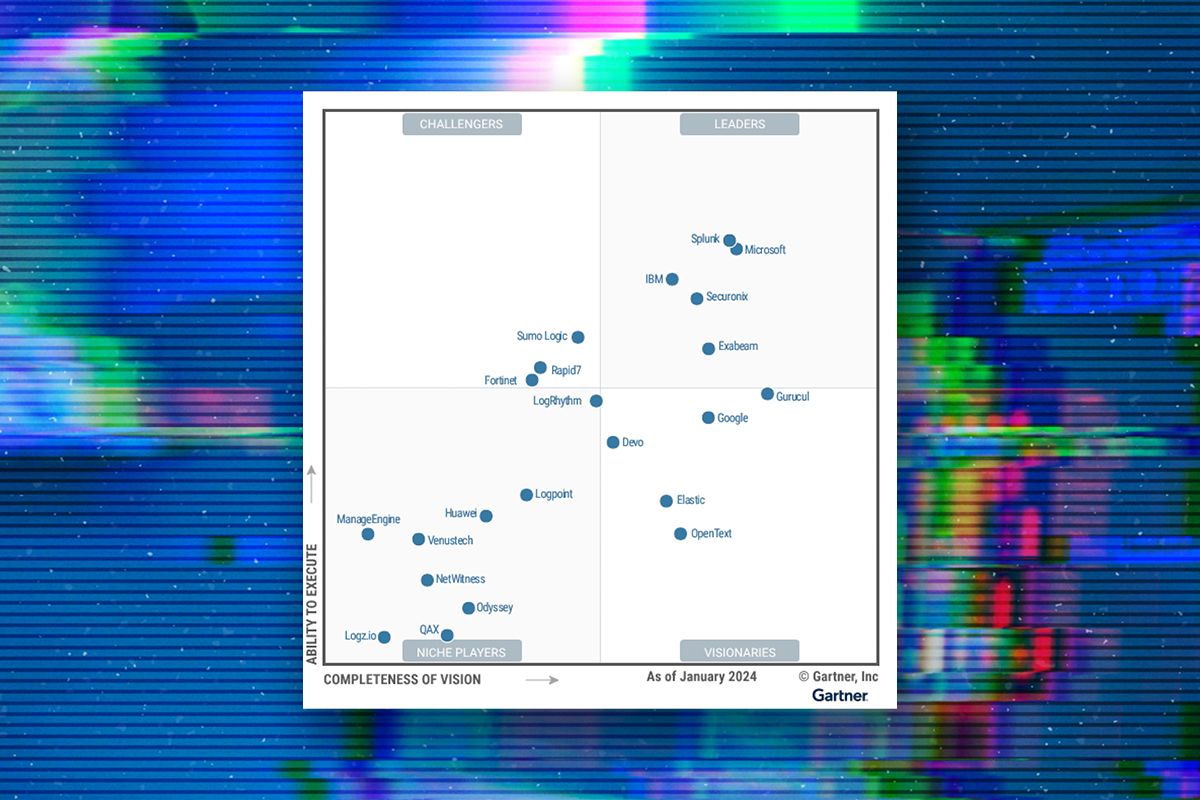
- Microsoft Azure Sentinel - io-xdr/), Splunk, Graylog.
- TIP
- TIP
SOC/CSIRT architecture of detection
- Gartner magic quadrant
- IBM Resilient - project.org/), SwimLane, PAN Cortex XSOAR
Critical tools for CSIRT
SOC architecture of detection
- Thor Cloud lite
- Cat-Scale
- Sysinspector
- Velociraptor
- DFIR-ORC
- Sysmon
- Semperis Purple Knight
- ADRecon
- Joe's sandbox - analysis.com/), etc;
- automation
- SIFT Workstation - linux.org/);
- Remnux
- Timesketch - iris.org/)
- CTI's repo
- Windows Defender Offline
- WithSecure Elements EDR
- Azure AD Incident Response Powershell
- ScootSuite
- UAC
- BloodHound Community
- CrowdStrike Reporting Tool for Azure
- 365Inspect
- FastIR - security/varc), FireEye Redline, DFIR-ORC;
- CIMSweep - Toolkit) but it relies on CrowdStrike EDR, GRR but it needs an agent to be installed.
- FireEye Flare-VM
- Loki - ORC](https://github.com/dfir-orc)
- Tiny Check
- Yara-rules GitHub repo
- Yara rules repo
- Community Yara rules
- Olaf Hartong's config
- Zircolite - blue-team/DeepBlueCLI), CrowdSec
- Sekoia XDR
- Powershell Hunter
- Sysinspector
- CISA Thorium
- WithSecure Elements EDR
- Semperis Purple Knight
- ADTrapper
- Tiny Check
SOC/CSIRT architecture of detection
Disconnect (as much as possible) SOC from monitored environment
Enclave:

Endpoints hardening:
- CIS benchmarks - us/download/details.aspx?id=55319)
For a CERT/CSIRT
- CERT-in-a-box
- CSIRT Services Framework
- Good practice for incident management
- Incident Response whitepaper
- SP800-86, integration forensics techniques into IR
- Incident response reference guide
- Security incident management according to ISO 27005
- Incident Response Playbook: Dark Web Breaches
- Incident Response playbooks
- Incident Response Playbook: Dark Web Breaches
- IR Mitigations tasks
- IR lessons on cloud ID compromise
- ForensicsArtefacts
- IR playbooks
- Incident Response whitepaper
- CSIRT Services Framework
- ForensicsWiki
- Incident Response
- IR phases
- Incident Response Methodology
For a SOC
- SOC-CMM
- Building a SOC
- ISO 27035 Practical value for CSIRT and SOCs
- SOC model guide
- Building a SOC
- State of Security 2023
- SOC model guide
- SOC model guide
- SOC analyst interview questions
- DeTTECT
- 2024 SOC survey
- SOC model guide
- Continous purple teaming
- Secure your business with 365
- SOC Metrics
- State of Security 2025
- 2025 SOC survey
Globally (SOC and CERT/CSIRT)
- Security 360
- Cybersecurity framework
- SP800-61 rev2, incident handling guide
- ATT&CK: Getting started
- SIRP / SOA / TIP benefits
- Cyber Threat readiness report 2023
- Market Guide for Security Orchestration, Automation and Response Solutions
- Security orchestration for dummies
- CVSS v4 specs
- STIX
- TLP - policy/)
- 18 critical security controls
- Cybersecurity business value benchmark
- NIS2, how to address the security control gaps
- What is SecOps
- Market Guide for Security Orchestration, Automation and Response Solutions
- Visual Threat Intelligence
- CSIRT, SOC, ISAC and PSIRT definitions
- Blue Team Notes
- SP800-61 rev3, incident handling guide
- Mappings explorer
- SaaS attack matrix
- Threat Matrix for Azure Storage services
- Threat Matrix for AI-systems
- Best practices for automating SecOps workflow
- "While the initial trigger event was a Distributed Denial-of-Service (DDoS) attack... initial investigations suggest that an error in the implementation of our defences amplified the impact of the attack rather than mitigating it"
- What is SecOps
- Compromise assessment methodology
- NIS2 10 main requirements
- How to set-up a CSIRT and SOC
- Market Guide for Security Orchestration, Automation and Response Solutions
- State of SIEM market 2025
- What is SecOps
- NIS2 technical implementation guidance
- What is SecOps
- Baseline Cyber Security Requirements for AI Models and Systems
- R 8596, Cybersecurity Framework Profile for Artificial Intelligence
- CTI Framework
- Turning threat reports into detection insights with AI
- How to set-up a CSIRT and SOC
- Top 10 for Agentic Applications
- Challenges to the Monitoring of Deployed AI Systems
- CTI Framework
- AI 100-1
- What is SecOps?
- SIRP / SOA / TIP benefits
- SecOPS vs. OPSEC
- SIRP / SOA / TIP benefits
- Threat hunting framework (PEAK)
- NIS2 webinar
- SOCs face a challenge as AI speeds alerts and threats
- ENISA's view on cybersecurity in the frontier AI era
- FAICP

Harden SOC/CSIRT environment
Endpoints hardening:
- CIS - us/download/details.aspx?id=55319)
- forest is the AD security boundary
- image
- Wallix PAM
- Microsoft Developer virtual machines
- script
- hardening tool
- Security Compliance Toolkit
- SP800-63B: Digital Identity Guidelines

**Miscellaneous Resources**
Have a single and centralized platform ('single console')
SOC architecture of detection
Must read
Endpoints hardening:
- 11 strategies for a world-class SOC (remaining of PDF)
- Cyber Defense Incident Responder role
- Purple Team Assessment
- AV / EP / EPP / EDR / XDR
- Security bastion (PAM) and Active Directory tiering mode: how to reconcile the two paradigms?
- list of Windows API and their potential use in offensive security
- OpenIOC format